
Insights & updates
Practical takes on ISO standards, GDPR, and how AI is automating the compliance lifecycle.
Latest articles
HEC Director and Delegation Explore AI Compliance Automation at NIC Karachi
During a recent visit by HEC Pakistan to the National Incubation Center Karachi, ComplyEncrypt founder SM Waqas Imam tackled a crucial question: why rely on dedicated compliance tools when standard AI chatbots like ChatGPT or Claude exist? Discover why generic AI fails during real-world audits and how purpose-built automation solves the context, hallucination, and traceability gaps.
Read article
Why a Chatbot Is Not a Compliance Department, and What ComplyEncrypt Does Differently
General-purpose AI can draft plausible policies. Compliance needs controlled, current and traceable records. Here is where chatbots fall short and what ComplyEncrypt does differently.
Read article
ISO 9001:2026 Is Here: What Has Changed and How AI-Assisted Compliance Automation Is Transforming Quality Management
ISO 9001:2026 was published on 16 September 2026. Here is what changed — quality culture, climate considerations, risk and opportunity clarity — and how AI-assisted compliance automation helps organizations prepare for the transition.
Read article
GDPR / ISO 27001 Compliance for Startups and SMEs in Industry 4.0
Pakistani startups hit a compliance wall the moment a European client asks for proof. A shorter look at why GDPR and ISO 27001 are now the entry ticket for Industry 4.0 businesses.
Read article
Compliance Is Not the Cost of Exporting IT Services — It Is the Entry Ticket
EU clients do not inspect an IT service on arrival; they audit its evidence. Here is the exact documentation pack a European controller demands — and how automation now cuts the cost of producing it.
Read articleHow to comply with ISO/IEC 27001:2022 Annex A controls
A practical, auditor's-eye walkthrough of the 93 Annex A controls — the four themes, the Statement of Applicability, and an eight-step implementation sequence that an in-house team can own end-to-end.
Read articleISO 14001:2026 — what changes and how ComplyEncrypt is preparing
ISO 14001 is being revised for 2026 with stronger climate, lifecycle and stakeholder requirements. Here's what to expect — and how the ComplyEncrypt team is integrating the new standard into our AI-automated workflow.
Read article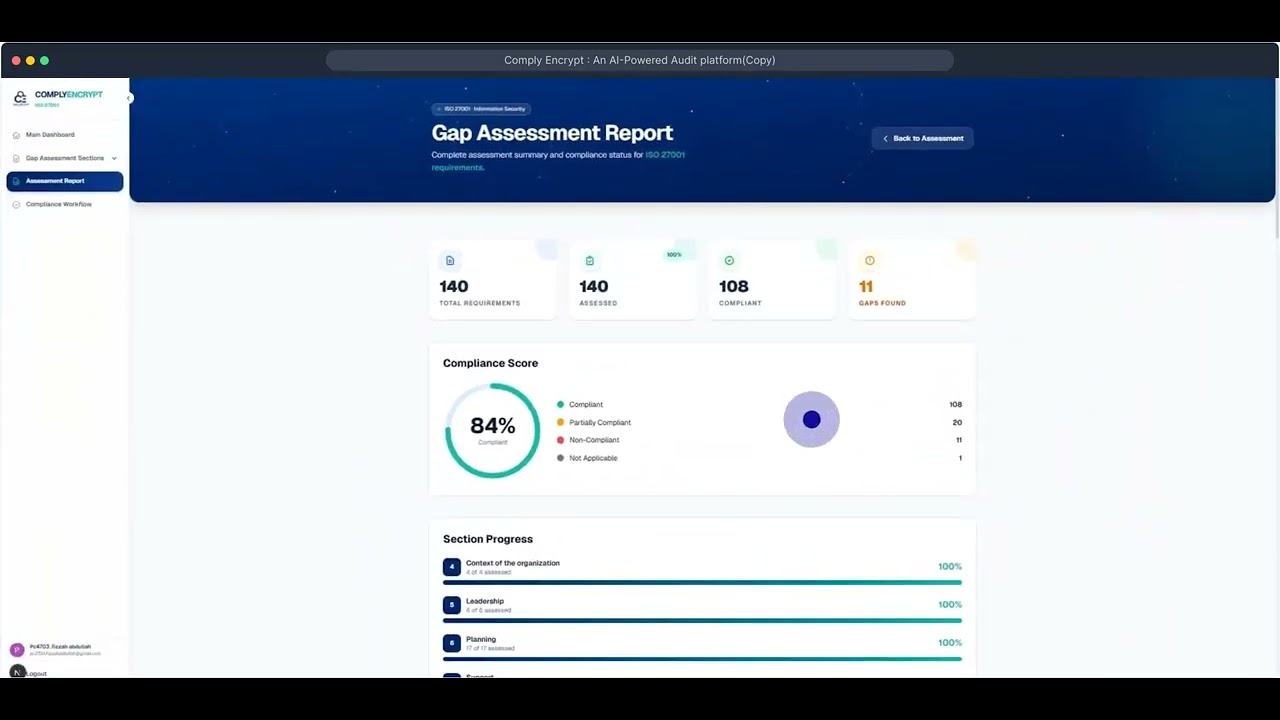
Introducing the ComplyEncrypt MVP
A walkthrough of our first release — what's inside, what it automates, and what's coming next. Includes the full MVP video.
Read articleISO 27001 & GDPR: Not a Monolith, a Modular Pathway
Why treating ISO 27001 and GDPR as one giant project fails SMEs — and how a modular, control-reuse pathway gets you audit-ready faster.
Read articleInformation Security Isn't an Option — It's the Operating Principle
Security as the operating principle of the business — not a quarterly project, not a checklist, not a cleanup before the audit.
Read article